Download Popular Antivirus Program

Tuesday, July 23, 2013
Delete Adware Generic5.ACKC Thoroughly: Manual Removal Method

Remove News.net Virus - Manual Removal
News.net is an adware inflection that can be categorized as a malicious browser hijacker. It will display annoying advertisements and news on infected computer. Once installed on your computer, the News.net malware toolbar will take over your web browsers, such as Google Chrome, Firefox and Internet Explorer to show you the commercial advertisements and unwanted stuff on your screen. More appalling, most users complain that News.net modifies their default search engine, browser homepage and vital settings without their knowledge and permission. The hijacker inflection will redirects you to the suspicious web sites which may ask you to install harmful freeware or even lure you to purchase some unwanted advertisements products. Besides, the News.net virus will track your online activities to collect information about your interests, so the browser hijacker maker can attack your system easily with its malware. Once running in your computer, News.net will block everything and fake security alerts will start popping up from everywhere. It is important to the users known that News.net is a nasty browser hijacker can attacks your system to make it poorly performed. This tricky browser hijacker slows down your system performance, and even it makes your computer freezing. Thus, to prevent damages to your system,you should get rid of News.net as soon as possible.
Sunday, July 21, 2013
Cannot Uninstall Coupondropdown. com (Useful Manual Removal)
Coupondropdown. com is a new malicious browser hijacker that displays advertisements and hijacks your browsers. As a tricky adware, it can avoid detection from your antivirus protection to display advertisements on your browsers. CouponDropDown is different from other adwares because it can use in-text advertisements similar to Text Enhance and can be voluntarily installed with third party applications. It can access into your computer through internet connection without your knowledge. CouponDropdown is an extension for browsers that is activated when you install other free programs, software, games, codecs and toolbars on your computer. This browser hijacker will then change your home page and your search provider into its own website. This type browsers hijacker tries all means to restrict you on its website by unwanted advertisements popups. What’s worse, CouponDropDown is not that easy to uninstall because at times it does not appear on the Control Panel and it hides within programs. So when you find uninstall suspicious or unknown toolbar or software on your computer, you should remove CouponDropDown no more delay.
Saturday, July 20, 2013
Remove Trojan:DOS/Alureon.E - Completely Delete and Get Rid of Trojan:DOS/Alureon.E
Trojan:DOS/Alureon.E is a horrible Trojan virus made by cyber criminals to attack innocent computer users without any early warning and precaution. This type Trojan settles itself down on a computer without permission. To be a stealer, it can steal the user personal information and confidential data stored on the computer. Trojan horse DOS/Alureon.E usually has a strong offensive to destroy information and files in a computer, resulting in the abnormal working of the computer, or more seriously, making the system unavailable. As one stubborn Trojan, it won’t leave the chance to the user to get rid of it. When it successfully comes into the users’ computer, Trojan:DOS/Alureon.E will pretend to start its righteous work. The infected computer users will lose their information when they found their personal information such as credit card number, bank account and social security number exposed to the public. Moreover, Trojan:DOS/Alureon.E will sneak into the computer system and open a backdoor on your computer that allows attackers to access and steal crucial data, delete important files and initiate additional attacks on the computer system and network that you use. So it is high time that you should remove Trojan horse DOS/Alureon.E to protect your computer from the damage of this tricky Trojan.
Friday, July 19, 2013
Learn to Remove Australian Communications and Media Authority (ACMA) virus Step by Step (Virus Removal)
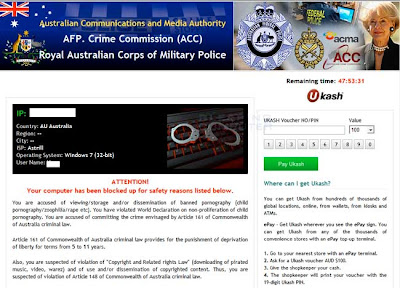
Australian Communications and Media Authority (ACMA) virus is a group of ransomware that uses the name of the government department to get users money in Australia. This virus locks victims computer and show a lock screen that requests a ransom of AUD $100 by Ukash before you can access your Window desktop. The ransomware program targets the Australian computer users in the names of the Australian Communications and Media Authority (ACMA), AFP Crime Commission (ACC), Royal Australian Corps of Military Police, and Interpol to scare its victims that your computer has been involved in illegal cyber activity. It is important to realize that this computer virus is only scam which can be ignored because the real government will not use this way to notice the people who have broken the laws. Let alone lock the users’ computer. The virus maker will plant this ransomware into the free program so that the victims’ computers are easily infected. When this type malware installed on the computer, you can’t do anything except on the screen is a fake warning that says you have violated laws and thus computer is locked up as a punishment. Moreover, this virus can slow your computer performance, and it can cause many serious computer problems. So when you suffer this situation about lock screen, you should not pay a fine to this virus. To get your computer in normal function, the effective way is manual removal this virus.
Thursday, July 18, 2013
The Effective Guide to Remove European Cybercrime Centre virus - Manual Removal Support
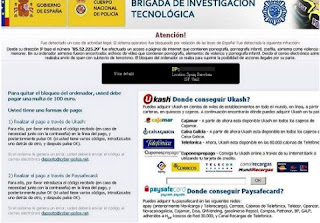
European Cybercrime Centre Virus can be categorized as a ransomware virus, which locks the computer and displays a warning page out of nowhere blocking you from accessing the browser as it’s taken up the full screen. It hides behind unsafe domain and pretends to be from the European Cybercrime Centre (EUROPOL) to require the users’ payment for they have violated laws by downloading pornographic material and copyrighted content. Actually the users don’t know what happen, but they really scared since it looks so real. This type ransomware virus can come with malicious websites, or legitimate websites that have been compromised. Spam email containing infected attachments or links to malicious websites also can propagate this type of ransomware. Some people may think they are installing the useful software when they download the malware. Once installed on the infected computer, the European Cybercrime Centre virus will lock your computer and applications, so when you are trying to log on into your Windows operating system or Safe Mode with Networking, it will display instead a lock screen asking you to pay a non-existing fine in the form of a Ukash or Paysafecard code. To make matters worse, this tricky virus also is able to control your installed webcam secretly, so you will suffer snooping attack. In order to protect your benefit from hacker attack, please get rid of European Cybercrime Centre virus as soon as possible.


Monday, July 15, 2013
How to Remove Websearch.greatresults.info Hijacker? Manual Removal
Websearch.greatresults.info is a tricky browser hijacker virus that can change the default settings of your browsers, such as Internet Explorer, Google Chrome and Mozilla Firefox. As if your computer infected with Websearch.greatresults.info, you will find that your homepage is changed, and it is no use to open the bookmarks instead of lots of advertisements popup. Your programs also stay in low performance, so you have to wait for a long time to install them. You can’t surf on the Internet normally because this type browser hijacker will take control of all your browsers. Once this redirect virus installed on your computer, it will make random trash files that results in your private files and secret information snooping. The virus makers can get your sensible information via using key loggers and keystrokes. So there is no security with your contacts, sent mails, drafts, inbox mails and spam box. Moreover, this nasty browser hijacker can spread secretly to make more people infect this redirect virus. It is dangerous that Websearch.greatresults.info can misdirect the victims to the illegal links, which contain many malware and other virus. When you don’t pay enough attention to this, you may click on a small box showing you only an OK button. When you want to close the window you will turn to another website, which declares to help you optimize your PC. If you follow the steps, you will be tricked by the program which you download because you will find that the program is hard to control. So when you find Websearch.greatresults.info on your computer, please remove it without hesitate.
Sunday, July 14, 2013
Need Help to Remove Mandiant U.S.A Cyber Security Completely: Manual Removal
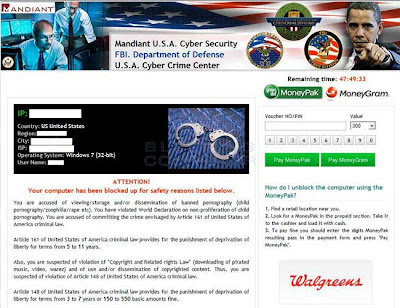
Mandiant U.S.A. Cyber Security is one type of Ransomware which displays a lock screen when you start Windows. It requires computer users among the United States areas to pay a ransom before you will be allowed to access your Windows desktop, applications, or files. It pretends to be Mandiant, the FBI, USA Cyber Crime Center, Department of Justice, and Interpol to block computers to get the victims to pay a fine in the amount of $300 within 48 hours. To make the victims firmly believe, this Mandiant U.S.A Cyber Security ransomware can state the reasons why your computer was blocked, such as the distribution of pornography, copyrighted files, or computer viruses, and it can list personal information like IP, Country, Region, City, Operating System and User Name etc on top left corner of the screen. The malware creators claim that you can access your Window desktop again when they receive the money through MoneyPak or MoneyGram voucher. Computer users log on to hacked or malicious sites online, download unknown spam attachments or install unfamiliar programs, they could get the chances to be infected by this tricky Ransomware. It is important to ignore this because Mandiant U.S.A Cyber Security is a computer inflection. It does not let your computer get right even if you pay for the fine. So when you suffer this problem, you should remove this Mandiant U.S.A Cyber Security ransomware quickly.