Download Popular Antivirus Program

Showing posts with label Manual Removal Support. Show all posts
Showing posts with label Manual Removal Support. Show all posts
Friday, August 22, 2014
Delete Trojan:Win32/Peaac Completely and Permanently – Manual Removal Support

Tuesday, June 17, 2014
The Effective Guide to Remove Lpmxp2014.com - Manual Removal Support
Lpmxp2014.com is a fake website that is designed to promote the internet traffic of certain websites. It usually bundles itself with spam e-mails, corrupt websites, freeware and other malicious downloads. If you carelessly execute the infected files, this redirect virus will seize the chance to enter your system. When you do online searches or click a sponsored links, it doesn’t present the correct page, but reroutes you to ads-related websites, which states that your computer was infected with Trojans, Spyware, rootkits, keyloggers, computer worms, etc. Once infected, it is so difficult for you to reach the expected domains. Because of Lpmxp2014.com virus, your browser will not work as properly as before. Moreover, hackers often take advantage of this fake website to steal data from the infected machine. It existence is a great threat to your privacy. Worse still, In order to help hackers’ make more money, Lpmxp2014.com virus usually steals financial data like online bank accounts, credit card details, and passwords. To prevent greater damage, it is strongly recommended you to remove Lpmxp2014.com virus as quickly as possible.
Friday, March 28, 2014
Remove Police Department University of California Completely and Quickly (Manual Removal Support)
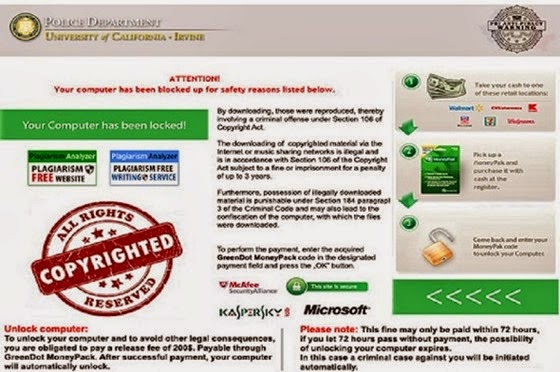
Police Department University of California is a computer ransomware threat that is presented in the form of a deceptive message, and it is designed to assault PC users located in California. This ransomware hides behind unsafe domain and locks your browser without notice. It pretends to be a real government statement to scare and deceive people by stating that PC users have violated Laws by illegal downloading or watching child pron. It makes PC users really scared since it looks so real! This virus will block browser immediately and make your browser useless. The only way to use it back is to reopen the browser which can be really annoying and inconvenient. Don’t believe it! It is a trick that created to collect money from innocent users. The only way to get rid of it is to use manual way to delete it. Once the Ransomware gets into your computer, it will enable the remote access from cyber criminals to the affected computer in order to violate your privacy and compromise your security. It goes on to state that the computer has been blocked up due to user’s cyber activities like downloading/viewing prohibited pornographic contents or using/distributing some copyrighted contents. Thus to unlock the blocked PC system and avoid the legal consequences, Police Department University of California virus demands users to pay a release fine of $200 through GreenDot MoneyPack or other anonymous online payment system. When you suffer this situation about lock screen, you should not pay a fine to this virus. In order to prevent hackers to steal your private information, you should get rid of Police Department University of California no more delay.
Saturday, November 30, 2013
The Effective Guide to Remove Nation Zoom - Manual Removal Support
Nation Zoom (also known as Nationzoom.com) is a browser hijacker that infiltrates into computer without users’ consent to make changes in all famous browsers. Usually, Nation Zoom is installed bundled with free software. Nation Zoom virus can take over Internet Explorer, Mozilla Firefox and Google Chrome. Once there it replaces your default search provider and start page. The website looks like a regular search provider. However, it includes tons of commercial websites to your search results and constantly tries to redirect you to some unknown websites. Basically, Nation Zoom virus makes money by increasing page ranking of several websites and from affiliate links. It also displays different ads on the infected system expecting users to click on them and make some more redirections. Each time your system is posing risk to get infected as you are not aware about the infections you can get by visiting unknown pages. Besides, the infected machine will run as slow as a snail and perform very poorly, because Nation Zoom installs lots of malware on the sly which take up a big part of system resources. Furthermore, in order to maximize hackers’ benefit, Nation Zoom will collect your confidential information and transmit those records to a remote sever. Therefore, to protect your benefit and prevent greater damage, it is important to remove Nation Zoom no more delay.
Wednesday, November 13, 2013
The Effective Guide to Remove Dingo Deals - Manual Removal Support
Dingo Deals is a browser extension that can access to computer without user knowledge. As a potentially unwanted program, it gets into your computer when you visit shopping websites, for example, Ebay, Amazon, Walmart, etc. if you click any suspicious icon or link, Dingo Deals will attacks all web browsers including the IE, Chrome, Firefox, etc. it will mess up your computer to cause quite annoying interruptions of your work online. Once installed, this adware has ability to change your browser settings and search provides. There will be lots of pop ups ads when you are browsing the web. If you click the ads windows, Dingo Deals will redirect you to a certain unwanted website that possesses various ads, coupons and deals, etc. moreover, this adware can be used by web criminals to spread harmful virus like Trojans, spyware and malware. It is very dangerous to keep this PUP on your computer. It will slow down your computer, and it can occupy high system resources. It will download its related files without user’s permission. In addition, Dingo Deals also collects information about your browsing habits for the illicit use. So , it needs to remove this nasty adware to stop pop ups and protect your computer.
Wednesday, November 6, 2013
The Effective Guide to Remove Central Security Service virus - Manual Removal Support
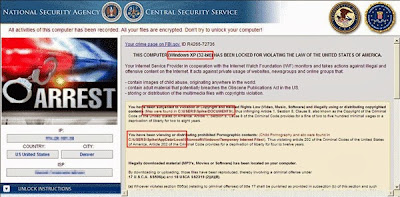
Central Security Service virus is a dangerous ransomware infection that blocks the user computer to attack the users in USA, and it disconnects your PC from internet. It displays a bogus full screen pop up warning message to make people think that Central Security Service noticed their illegal online activities. It distributes via the Urausy Trojan, which blocks the target computer user from accessing the desktop. Once Central Security Service virus sneaks into your system successfully, it will quickly alter system settings and lock your screen. As a result, you will be forbidden to access the PC. In order to threaten you, Central Security Service generates a fake notification which says that your PC is locked due to distributing illegal stuff. And it requires you to pay a fine, which demands a ransom of $300 to be paid via MoneyPak or MoneyGram to restore access to the computer system. However, before you make this payment, you must realize that this warning message belongs to scammers that seek to swindle the money from you. You must ignore fake alert that blocks your computer and remove Central Security Service virus from the system because it is a fake pop up alert of Central Security Service. Thought it blames computer users for performing a variety of illegitimate, you should not be scared by this online scam. Instead of the scare, you are supposed to find an effective way to remove the Central Security Service virus as soon as possible.
Sunday, November 3, 2013
The Effective Guide to Remove Rvzr-a.akamaihd.net - Manual Removal Support
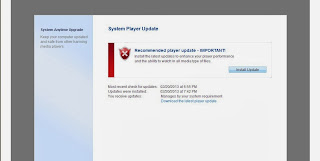
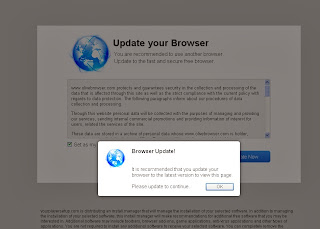
Rvzr-a.akamaihd.net is a pop up virus that appears on a computer when its hijacked by a browser infection named http://rvzr-a.akamaihd.net/sd/wrap-0.01.html?u=http%3A%2F%2Frvzr-a.akamaihd.net%2Fsd%2Fapps%2Ffusionx%2F0.0.4.html%3Faff%3D1700-1019. It is a corrupt plugin/extension which can target a Firefox, Chrome or Internet explorer user without his knowledge. Rvzr-a.akamaihd.net may have infected your computer, and then you’ll get to know about this bug when all of sudden you see advertisements by Rvzr-a.akamaihd.net keep popping up on your screen. After getting installed, it has the ability to change the browser settings including default search engine, home page, and privacy settings to take the complete control of your browser. It has the ability to modify the existing registry entries, and create the new corrupt entries so that it can start itself every time you open the windows. It has the ability to change the security settings by disabling the antivirus program installed in your computer due to which the system becomes vulnerable to the other similar threats. It will prompt you to with some fake pop-ups Windows that indicate your system get infect or it needs to software update but it all are scam. Hence, it is very important to remove Rvzr-a.akamaihd.net for your PC safety.
Tuesday, October 29, 2013
The Effective Guide to Remove Backdoor.Win32.ZAccess.eooq - Manual Removal Support
 Backdoor.Win32.ZAccess.eooq is a nasty Trojan horse which detected by the Microsoft Security Essentials or other antivirus. This type of Trojan has ability to allow a remote attacker to gain access on the infected PC. It is dangerous that the user don’t know the location of the hackers when they stage a number of actions after the connection has established. It is also allow the unknown link to download arbitrary files causing more damages on the infected system. Once Backdoor.Win32.ZAccess.eooq is executed, it will download a copy of virus file under various folders and system directories. As a stubborn Trojan horse virus, it creates a number of registry entries to allow itself to run each windows starts. Because of the modification on the registry, Backdoor.Win32.ZAccess.eooq can bypass windows firewall to allow transmission over the existing network. Besides, this backdoor Trojan can access your system without the user consent. It plants harmful files and steals sensitive data from victim’s computer. It can involve in file transfer and file deletion, and it also terminates some programs on the affected PC. In order to protect your computer from the damages, you are supposed to be aware of the infection. Manual removal is the effective way to remove the Backdoor.Win32.ZAccess.eooq from the infected computer completely.
Sunday, October 20, 2013
The Effective Guide to Remove www.search-guru.com - Manual Removal Support
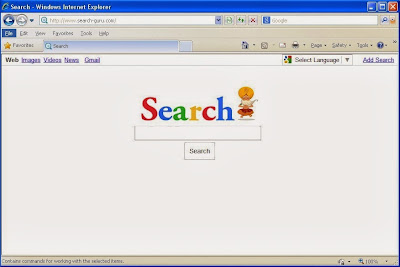
www.search-guru.com is a newly browser hijacker that changes internet browser settings of Google Chrome, Mozilla Firefox , Microsoft Internet Explorer and all other famous web browser programs. www.search-guru.com will enter your system without being detected by your antivirus program via free resource downloads, risky websites, and free videos. Once this hazardous infection infects your system, it will alter the default settings of your browser, so as to occupy the browser, such as Google Chrome, Internet Explorer, and Mozilla Firefox. Moreover, www.search-guru.com will change your homepage and default settings without your approval. In this way, it can lure you visiting its malicious websites frequently, which will generate more traffic. Then the creators will convert the inflated traffic into money and make a profit. What is more, www.search-guru.com will pop up lots of annoying ads to drive you crazy. No matter when you browse on the websites, pop-up ads often appear on your screen. In addition, this harmful virus will infect the system files and make some of the important programs disable, which is really annoying. The most troublesome issue is that www.search-guru.com may download many other viruses onto the system later, which can ruin the system and make the computer disable forever. Hence, for the safety of your machine, you must remove www.search-guru.com right away.
Saturday, October 12, 2013
The Effective Guide to Remove Websearch.searchthere.info - Manual Removal Support
Websearch.searchthere.info is a harmful browser hijacker that assails all well-known web browsers including Internet Explorer, Chrome and Firefox. It modifies default search engine and homepage settings. This homepage hijacker is bundled with freeware to promote websearch.searchere.info and to make money using advertisements within the search results. It is competent of collecting your browsers activities and sends it to distant server sponsoring related and unwanted ads. The search results that it shows are constantly inappropriate and packed with ads and sponsored links. Once you search using websearch.searchere.info your search term is redirected to random search engines, the performance of your windows system will degrade enormously. As a nasty browser hijacker, Websearch.searchthere.info pretends to be a usual website that looks like as legal as other legitimate website so you may not aware of its large amount of adware and the fact that it may contains malicious free links behind. To be worse, Websearch.searchthere.info automatically installs various files which may contain key loggers to record your browsing history and steal username and password when the user fill it in the websites. It tricks the innocent user by its appearance, which it is a useful search engine like Google.com. So, if you have also seen these activities on your computer, then it is very much advised that you remove Websearch.searchthere.info from your computer system immediately.
Tuesday, August 20, 2013
The Effective Guide to Remove Web.tofushopnews.com - Manual Removal Support
Web.tofushopnews.com is a risky browser hijacker that changes the homepage and default search engine of all your browsers like Internet Explorer, Google Chrome, and Mozilla Firefox without permission and approval. The web.tofushopnews.com software is usually distributed through malicious websites and comes with free programs that users download from the Internet. As a stubborn redirect virus, it was widely discussed for its fully commercial pop up, annoying redirects and homepage hijacking to web.tofushopnews.com domain. Once infected, Web.tofushopnews.com may automatically install more infections like Trojan, worms, key loggers and other spywares. The compromised computer may experience slow internet running, freezing browsers, blue screen of death, new desktop background and unfamiliar free software shortcut. However, the protection program may detect nothing and this web.tofushopnews.com virus still redirect your homepage and displays unwanted pop-up ads. What’s more, in spite of web.tofushopnews.com seems just a normal website but do not fall for its interface, it can drop cookies and use other techniques to track your activities, collects your financial information and may invite further viruses and spywares from Internet. You must uninstall Web.tofushopnews.com virus and remove its corrupt configurations from your browser.
Thursday, July 18, 2013
The Effective Guide to Remove European Cybercrime Centre virus - Manual Removal Support
European Cybercrime Centre Virus can be categorized as a ransomware virus, which locks the computer and displays a warning page out of nowhere blocking you from accessing the browser as it’s taken up the full screen. It hides behind unsafe domain and pretends to be from the European Cybercrime Centre (EUROPOL) to require the users’ payment for they have violated laws by downloading pornographic material and copyrighted content. Actually the users don’t know what happen, but they really scared since it looks so real. This type ransomware virus can come with malicious websites, or legitimate websites that have been compromised. Spam email containing infected attachments or links to malicious websites also can propagate this type of ransomware. Some people may think they are installing the useful software when they download the malware. Once installed on the infected computer, the European Cybercrime Centre virus will lock your computer and applications, so when you are trying to log on into your Windows operating system or Safe Mode with Networking, it will display instead a lock screen asking you to pay a non-existing fine in the form of a Ukash or Paysafecard code. To make matters worse, this tricky virus also is able to control your installed webcam secretly, so you will suffer snooping attack. In order to protect your benefit from hacker attack, please get rid of European Cybercrime Centre virus as soon as possible.