Download Popular Antivirus Program

Showing posts with label a Trojan horse. Show all posts

Tuesday, September 2, 2014

[Efficient Removal Instructions] Delete Trojan horse Downloader.Generic10.UIK Infection Permanently

Description of Trojan horse Downloader.Generic10.UIK


Trojan horse Downloader.Generic10.UIK is classified as a hazardous Trojan infection which comes with spam email attachments, suspicious websites and other malware. It opens a back door on the corrupted computer. It enables cyber criminals to obtain full remote access and control over the infected computer. Once this Trojan horse has entered your system, it will proceed to reedit your registry so that it will be able to start together with your system at all times and hide from your antivirus. This infection helps the cyber criminals to steal your personal and financial information which are stored in the computer without your knowledge. It means that its server uses a backdoor to spy on a user, manage files, install additional software or dangerous threats, and control the entire system. Moreover, this infection causes a series of severe problems like corruption of registry files, data lose, software failure and corruption in antivirus software. Therefore, it is very important to remove this Trojan horse Downloader.Generic10.UIK infection to protect your computer.

Monday, September 1, 2014

Permanently Removed! Remove Trojan:Win32/Anaki.A


Description of and Trojan:Win32/Anaki.A


Trojan:Win32/Anaki.A is recognized as a dangerous Trojan horse which created by cyber criminals to affect computer. Usually this type of virus is spread on the internet via spam email attachments, suspicious websites and unknown free software. when it intrudes successfully into your computer, it will injects the harmful files to the system registry. Once after the execution, it keeps locating components on different system folders with files’ name. As a hazardous Trojan virus, Trojan:Win32/Anaki.A is able to change the computer security settings to cause malfunctions to the installed antivirus and anti-spyware. And then it creates system vulnerabilities in the affected computer. It is able to download other infections and steal your sensitive information such as your passwords, credit card numbers and login credentials. It will not only destroy your machine but also violates your privacy and compromises your security. In this situation, it is risky for user’s personal information to be exposed to the cyber criminals. Thus, it is necessary to remove it before it causes great damage.

Friday, August 29, 2014

Permanently Removed! Effective Removal Instructions for Trojan.Win32.Webnaviscan

Trojan.Win32.Webnaviscan is a noxious Trojan infection which is designed by cyber hackers to disguise itself as harmless and beneficial programs. On the contrary, you are instead installing a piece of malware that has a hidden purpose to perform harmful actions on your computer. This Trojan horse always gets into the target computer via clicking on spam email attachments or malicious links from websites. People who are careless about the online activity can be easily attacked by this infection without any permission. Once executed, this Trojan horse is capable to install backdoors so that the cyber hackers can access your computer, monitor your computer activities and execute commands on your computer remotely. Thus other malware can be downloaded into your computer, for example, a ransomware can be downloaded to encrypt all your important files and then blackmail you to pay the ransom in order to receive the key to decrypt them. As it can monitor your computer activities, it can steel your bank card accounts and their passwords and then withdraw all your money without your knowledge and consent. To make it be simple, this Trojan infection can be a dangerous thing that can seriously damage the infected computer and needs to be removed as soon as possible.

Thursday, August 28, 2014

Completely Removed! Effective Instructions to Get Rid of Trojan BHO.WPO

Description of Trojan BHO.WPO


Trojan BHO.WPO is recognized as a nasty and strong Trojan horse infection that may load in your computer from a malicious source on the Internet. When loaded, this infection will not show up to let you see it. It always hides in some free programs with interesting functions to attract you to download it into the computer. In addition, if you visit malicious websites that pops up unknown windows or asks you to install unknown plug-ins, your computer may also be infected once you click on them. Then it will install without your permission. Cyber criminals who design Trojan BHO.WPO are able to access and control the infected computer with the help of it. Once they connect to the computer successfully, they will have the chance to collect your valuable information or even monitor what you are doing in the computer. Thus, the cyber criminals can steel your important information and sensitive privacy easily. Besides, this malicious Trojan horse can sneak into your system and modify your registry. Your system will run lower than before and often end up with crashes. What is worse, this Trojan infection may download a ransomware to lock up your important files so that you can do nothing. To make it be simple, this Trojan BHO.WPO can be a dangerous infection that can damage the infected computer severely which needs to be removed as quickly as possible.

Saturday, May 25, 2013

How to Get Rid of Trojan.Zeroaccess!inf4 Virus - Remove Trojan.Zeroaccess!inf4 Virus Completely


Trojan.Zeroaccess!inf4 is a complicated Trojan horse which is highly crafty and stubborn to be seldom handled by antivirus software completely. The virus carries with multiple components that the common ways in dealing with computer virus won't be available. It is vital for users paying attention on suspicious links, pop-up advertisements and spam email files online. Try your best to keep computer free from the virus.

If by chance computer has been infected with Trojan.Zeroaccess!inf4 virus, it will be a tough experience to pass it through. The virus is found to take up system resources, slow down computer performance, affect system files and block system programs. What's worse? Trojan.Zeroaccess!inf4 exploits system with unauthorized backdoor access to bring computer with other infections gradually. It highly threatens to computer's security that it's not a good idea to remain it on computer for a long time. To the opposite, it is strongly advised to get Trojan.Zeroaccess!inf4 removed as soon as possible.


Snapshot of Trojan.Zeroaccess!inf4


Tuesday, May 14, 2013

Effective Remove ZeroAccess Rookit - How to Remove Manually and Completely


ZeroAccess is a highly risky rootkit virus that lasts long online to keep damaging thousands of computers across the world. Constantly, it mutates into different system files that make antivirus programs hardly remove it once for all. In addition, the infected files can be also diverse according to the types of operating systems.

Apart from the stubbornness and cunning, ZeroAccess is also found as offensive to modify system settings by generating harmful codes into registry entries and core of system part. By doing this, it is about to load up automatically together with the Windows to initiate malicious behaviors. Unauthorized access can be exploited for allowing other infections to come and destroy system files gradually day by day. There may come out system errors, homepage hijack or even blue screen of death.

Generally, ZeroAccess can be distributed via spam email attachment, peer-to-peer sharing or malicious websites. Even though the crafty virus is protected with rootkit skill which protects it from antivirus programs well, users need to work hard to exterminate ZeroAccess as early as possible for avoiding system data from lose.

Tuesday, May 7, 2013

Trojan horse PSW.OnlineGames4.ALGT Removal Guide - Remove Trojan horse PSW.OnlineGames4.ALGT Completely


Trojan horse PSW.OnlineGames4.ALGT is one of the members which come from Trojan horse family to carry out a series of detrimental damages on users' computers. All the harmful traits that it leaves on computers point system files into great dangers of being deleted, which to result in computer invalid to start. Judging from the name of Trojan horse PSW.OnlineGames4.ALGT, you can figure out that this dangerous virus is dropped for the purpose to steal users account and password from online games by hiding secretly in the core of computer with the disguise of system file format. In general, antivirus software won't be able to pick up the infected files and get them removed completely.

Besides the above, Trojan horse PSW.OnlineGames4.ALGT has been classified to open back door security vulnerabilities in an attempt to download computer with outside malware to enlarge the damages on system files. It goes without saying that computer performance will be largely decelerated and more troubles will be flooded into the compromised PC to drive users mad. In short, users are advised to remove Trojan horse PSW.OnlineGames4.ALGT virus as early as possible before any big trouble has been made.

Saturday, May 4, 2013

Guide to Remove TR/ATRAPS.Gen2 Virus Completely - How to Get Rid of TR/ATRAPS.Gen2


TR/ATRAPS.Gen2 is ranked to a high level risky Trojan horse that keeps hidden on computers for doing destroyable activities. The annoying point for this virus lies in its stubbornness which can not be easily handled by security tools. As a consequence, it keeps coming back time after time again when the computer has been rebooted.

Actually, TR/ATRAPS.Gen2 is a variant that originates from the hazardous family of TR/ATRAPS. Though there have multiple variants which are similar to it, the payloads and symptoms wouldn't be the same. However, it typically mutates frequently with the cover of system file format to evade the removal from antivirus programs for allowing it hanging around on system successfully. Registry entries as well as many other programs will be deactivated to cause poor computer performance.

To make matter worse, there is the trend that possibly taken by TR/ATRAPS.Gen2 to leave system with security flaw to make computer vulnerable for other treacherous infections. Undoubtedly, there will be flooded with much more severe troubles which may even lead to system crash. Kindly, for the consideration of PC's safety, TR/ATRAPS.Gen2 should be eradicated as quickly as possible.

Sunday, April 28, 2013

How to Remove zeroaccess.hi Virus - Manually and Completely Uninstall zeroaccess.hi


zeroaccess.hi that the very dangerous Trojan horse is not as small an issue as your expectation. This virus always comes into computer for doing annoying activities to get computer chaos. Antivirus software can detect it only but never get it removed thoroughly since it is tricky enough to bypass security tools by hiding malicious components successfully with rootkit skills. Users are required to pay close attention on all the downloads that come from the third party websites and never click on malicious links before making sure on them.  According to research, zeroaccess.hi is found to seriously impact computer performance by messing registry entry with malicious components. Worse still, unknown malware such as browser hijacker can be also downloaded to replace your homepage and redirect online searches frequently. Any delay to remove it may cause personal information exposure or even system crash. It is not a wise decision to leave it on computer for long. To make sure for the security of computers, users must move up to exterminate it as soon as possible.

Saturday, April 27, 2013

Way to Remove Win32/Small.CA - How to Get Rid of Win32/Small.CA Effectively


Win32/Small.CA is a detrimental Trojan horse which runs harmful damages on computers and cause abnormal activities. This threat always has the ability to hide itself with rootkit technology that the originated files can’t be found easily by antivirus software. In a general way, Win32/Small.CA injects into computer by the spread of exploiting software and other viruses via the security flaw. Even though it can be detected by reputable security tools, users won’t be able to get out of this issue completely.

As long as the installation, there will be numerous infected files added into the system to mess up system by starting with a series of violation. It will decelerate computer performance, block down program, turn off firewall to download undesired destructive programs to make computer seriously poor in security defense. It may even break essential system files to crash system down. For the concern of computer’s security, it is strongly advised to deal with Win32/Small.CA removed as early as possible.

Thursday, April 25, 2013

Effective Way to Remove Trojan horse Patched_c.LYU Virus


Trojan horse Patched_c.LYU is not only a dangerous Trojan horse but also an exceedingly stubborn virus that makes harmful violation on users' computers. To get into computer significantly, component of Trojan horse Patched_c.LYU will always be bundled with corrupted free programs, spam email attachment as well as malicious website. In this way, it can bypass through notice to users significantly.

According to the fast changeable traits, Trojan horse Patched_c.LYU is not an easy issue that to be removed thoroughly without paying hard work. It is extremely stubborn that always driving users crazy in picking up the infected files and stop it from coming back after every system reboot.

In the meantime, Trojan horse Patched_c.LYU will deeply hide components into the core of system part by the cover of rootkit skills. It stealthily changes system settings without asking permission that makes program files abnormal in response. The computer performance and network speed will be also affected seriously. In addition, if not to remove it timely, Trojan horse Patched_c.LYU can also breach firewall and system backdoor to bring in hazardous programs for doing unbelievable damages on the compromised PC. To sum up, due to the bad behaviors to Trojan horse Patched_c.LYU that never wait to remove this virus until it is too late.

Sunday, April 21, 2013

Best Way to Remove HEUR:Exploit.Java.CVE-2012-0507.gen Virus Completely


HEUR:Exploit.Java.CVE-2012-0507.gen is a highly threatening Trojan horse that has the ability to insert into computer by making use of exploiting free programs and malicious links created by online attackers. Carrying with rootkit component, HEUR:Exploit.Java.CVE-2012-0507.gen is able to keep the infected files which are located in the essential part of system hidden to escape removal from antivirus software significantly. That’s the reason for security tools fail to get this virus removed thoroughly. Normally, HEUR:Exploit.Java.CVE-2012-0507.gen can be loaded up automatically with the Windows attribute to the codes that it drops into the registry entries and Startup programs. Computer will become disorderedly and run into poor performance. Moreover, HEUR:Exploit.Java.CVE-2012-0507.gen is known to block firewall and exploit system with security flaw to download other type of infections to get computer seriously attacked or even invalid to run. All the important system data will be forced to destroy. Thus, for the sake of computer’s security, it is kindly recommended to get HEUR:Exploit.Java.CVE-2012-0507.gen removed as quickly as possible.

Thursday, April 11, 2013

How to Remove Trojan horse Generic29.AJGE Permanently


No need to say, Trojan horse Generic29.AJGE is a vicious Trojan horse that causes lists of annoying destructions on computers. Though it has many similar variants that come from the same infamous family, Trojan horse Generic29.AJGE seems to be too stubborn to get removed by antivirus software.

Users who get infected with this virus must be curious about the way it downloads into computer since it can't even be caught by antivirus programs. Actually, Trojan horse Generic29.AJGE always downloads into computer by attaching malicious component with many free application programs that published by the third party website. By the way, malicious websites, spam email attachment and other malware are also supposed as the ways for Trojan horse Generic29.AJGE installing into computer successfully.

Tuesday, April 2, 2013

How to Remove Trojan:DOS/Alureon.A Virus - Uninstall Trojan:DOS/Alureon.A Completely


If you are the one who is bothered by Trojan:DOS/Alureon.A virus, you can know how that would be upsetting to go through with this lousy threat. It is not surprised for the failure of removal to this virus by antivirus programs since Trojan:DOS/Alureon.A is crafty enough to know that how to keep it hiding among system files significantly. If the main file of the virus that can't be deleted, the replicated files will come back again after the every system reboot. Every after the execution of Trojan:DOS/Alureon.A, CPU usage will be noticed to reach to a high degree and everything would run weirdly and slowly. What's more, Trojan:DOS/Alureon.A is blamed for downloading additional malware such as browser hijacker, adware and rogue program to enlarge damages on user's PC or make it even invalid to work.

Saturday, March 30, 2013

Remove TR/Pirminay.aehr Virus Manually - How to Get Rid of TR/Pirminay.aehr

TR/Pirminay.aehr is a nasty Trojan horse which can be installed into computer both with the help of free programs and other malware which has been already stayed in computers. Due on the stubbornness to of this virus, it drives thousands of users crazy to go through with its removal but still with little effectiveness. Generally, users pick up this virus always through some of the sponsored links in social network like Facebook, Twitter or spam email attachment. It is necessary to keep an eye on unfamiliar links and do not click on them casually.

By changing various settings on system, TR/Pirminay.aehr is intended to make chaos on computers on both running performance and security defense. Computer will be noticed to respond in slow speed and retard to respond. What's more, anther annoying thing - redirect virus can be also dropped to take control your browser homepage and assist cyber criminal to gain personal information for implementing illegal activities. Evidently, such kind of detrimental virus can definitely not to keep in computers. Users must remove it completely as soon as you can.

Saturday, March 16, 2013

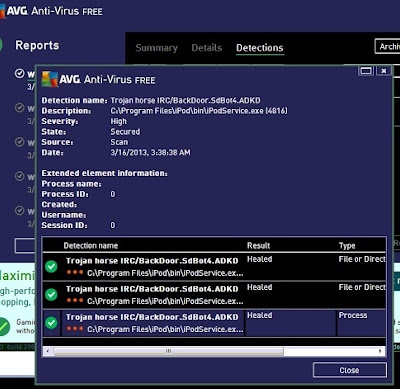
Best Way to Remove Trojan horse IRCBackDoor.SdBot4.ADKD Virus

What Is Trojan horse IRCBackDoor.SdBot4.ADKD? 


Trojan horse IRCBackDoor.SdBot4.ADKD is a pernicious Trojan horse which is treated as harmful as other similar variants such as Trojan horse IRCBackDoor.SdBot4.ACVN, Trojan horse IRCBackDoor.SdBot4.ACUL and Trojan horse IRCBackDoor.SdBot4.LHN. If you have tried to remove the virus with antivirus software, you must have experienced a hard time to try to fix this issue but the virus is still there. It is true that Trojan horse IRCBackDoor.SdBot4.ADKD has been covered with advanced tactics to make it succeed in concealing its infected files into different locations in the form of system files so that security tools are always not taken granted for the removal of this virus.

Friday, March 8, 2013

How to Remove Sirefef.gen!c Virus - Get Rid of Sirefef.gen!c

Sirefef.gen!c belongs to highly threatening Trojan horse which is known as a variant of Serefef family to affect most of the vulnerability-existed systems and insert computer with lots of inconvenience. Accordingly, the occurance for the virus can be always categorized to the wrong operation on spam email attachment, malicious links or corrupted programs. Users need to be vigilant while clicking or downloading something from the Internet.

Sirefef.gen!c is a big deal to the computer that users find it hard to be dealt with by security programs. It is able to make copies on the operating system with random file names to conceal its existence and take place for harmful damages to drive computer disorderedly. CPU usage will be noticed to pull up to high degree, programs fail to respond smoothly, fake error pops up or even system freeze.  What's terrible, Sirefef.gen!c is found to stop firewall to download unfamiliar malware into computer to enlarge the system attack. Computer may even get crashed down and make you lose important data. Thus, for the sake of the security of computer, Sirefef.gen!c must be terminated as fast as possible.

Monday, March 4, 2013

Best Way to Remove Exploit: Java/CVE-2012-5076.GAA Virus

Details about Exploit: Java/CVE-2012-5076.GAA


Exploit: Java/CVE-2012-5076.GAA is detected as a stubborn Trojan horse which installs into computers in the form of Java Script file along with other free programs. Due to the changeable and tricky characteristics, it makes difficulties to pick up all the infected files and have Exploit: Java/CVE-2012-5076.GAA removed completely by utilizing antivirus software, even which has been updated to the latest version.

Exploit: Java/CVE-2012-5076.GAA is a complex virus which is consisted of multiple components. With the components, it is able to disguise itself into random files and keep it ignorable to the antivirus software to gain long existence on computers. The virus is also found to insert system with malicious codes to smash the integrity of the running system. Computer performance will be obviously decelerated or even freeze to respond. To make matters worse, Exploit: Java/CVE-2012-5076.GAA has the ability to exploit system leaks, makes computer vulnerable to additional malware to make problem much more complicated to fix.