Trojan Horse Generic17.AMPT is nasty computer threat which automatically enters your Windows PC without any consent. Your AVG will keep alerting you with popup at low right corner of your screen over and over again at each minute, making your system slow and crash. Usually Trojan Horse Generic17.AMPT makes use of the social network accounts (Facebook, Twitter, MSN, etc.) to expand its influence. It alters the settings, so that the hijacked accounts will send malicious links to associated users. Once infected, Trojan Horse Generic17.AMPT can trigger a series of terrible problems, such as BSOD, freezes, system errors, crashes and Internet connection failure. If you ignore these problems and don’t take immediate action to fix them, your PC may completely break down in a short period. What’s more, as a typical Trojan virus, Trojan Horse Generic17.AMPT is used by hackers to steal data from the infected PC, which means all your privacy is seriously endangered by this Trojan virus, and hackers also can access your system via the vulnerabilities created by Trojan Horse Generic17.AMPT virus. It is a really risky infection, and in order to prevent greater damage, it is recommended to remove Trojan Horse Generic17.AMPT as soon as possible.
Download Popular Antivirus Program

Wednesday, April 30, 2014

How to Remove lpcloudbox326.com - Guide to Get Rid of lpcloudbox326.com Easily
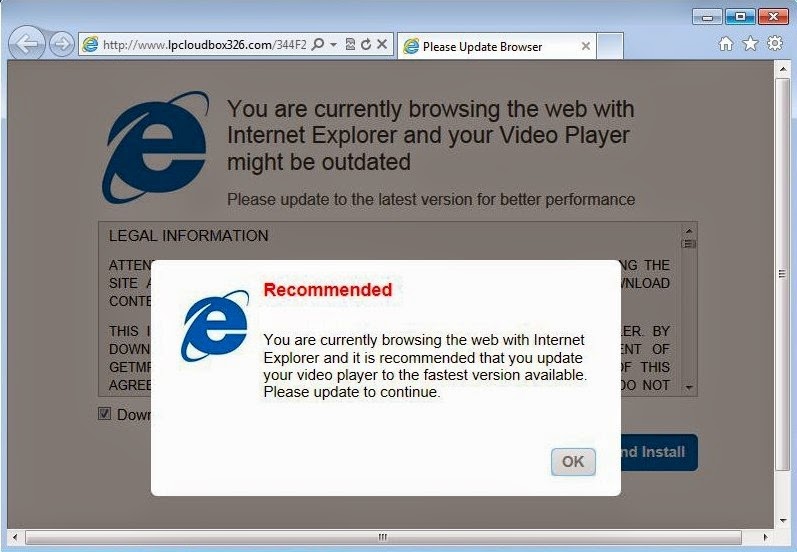
lpcloudbox326.com is a notorious browser hijacker redirection virus which will alter your homepage and slow down your computer’s performance. It is competent in dropping other malicious components like malware or Trojan horses onto the affected machine so as to produce further damage for the victims. Once the lpcloudbox326.com runs through you system, can also destroy your network and delete some critical files. It can do more except acting irritating. It can corrupt your PC like disabling your system registry and destroying computer files. lpcloudbox326.com also can collect your personal details as well as financial details without your knowledge and makes benefits from it. Most of the people go through browsing malicious webpages through their computers which are completely contained with various malicious agents which enters the PC while browsing, and make various unintentional changes in the system settings, browser settings, and Windows Registry settings. Since these settings in computers are essential to run the PC efficiently, if something goes wrong with them, it’s obvious for system get infected with lpcloudbox326.com. So, if you have seen this redirect virus on your computer, then it is very much advised that you remove lpcloudbox326.com from your computer system immediately.
Monday, April 28, 2014
How to Completely Get Rid of static.onlinefastpaydayloan.com popup (Step-by-Step Instructions)
static.onlinefastpaydayloan.com popup is a browser hijacker that can be added to Internet Explorer, Mozilla Firefox or Google Chrome without computer users’ knowledge and that tries to implement its malicious plans of generating numerous ads and distributing potentially unwanted programs.You may not be able to access any of the computer utilities like Task Manager, Registry Editor or others, as all of them might be deactivated. It is shaped so cleverly that it could simply dig out the loopholes in your computer system.
If your system has already been infected, you will be constantly receiving static.onlinefastpaydayloan.com popup offering you to update your Java or other legitimate program. However, if you follow what this message says you will actually agree to download a completely different program. This malware will flood your system with unwanted ads, fake update messages and redirect you to unwanted websites or even install other unwanted programs without your permission. Additionally, it can track your browsing history and record the information about your search queries. As a result, you may receive more targeted ads in future and you may be involved into other projects by the third parties.
static.onlinefastpaydayloan.com popup makes path for the other harmful malware or threats to get into the computer system and exploit it ruthlessly. It slows down the performance of the computer regularly and also hinders Internet accessibility in an improved manner. You will find it hard to use your computer system resources entirely as they were exceedingly confronted by the irritating windows system threats. In fact your important functionalities or other traits related to the system will also be disabled automatically. So, it is recommended to remove static.onlinefastpaydayloan.com popup from computer system as quick it is noticed.
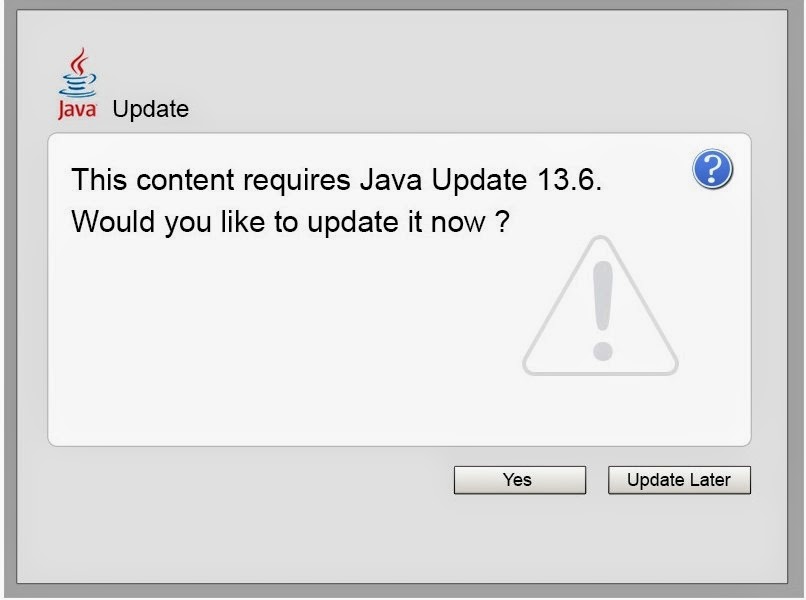
If your system has already been infected, you will be constantly receiving static.onlinefastpaydayloan.com popup offering you to update your Java or other legitimate program. However, if you follow what this message says you will actually agree to download a completely different program. This malware will flood your system with unwanted ads, fake update messages and redirect you to unwanted websites or even install other unwanted programs without your permission. Additionally, it can track your browsing history and record the information about your search queries. As a result, you may receive more targeted ads in future and you may be involved into other projects by the third parties.
static.onlinefastpaydayloan.com popup makes path for the other harmful malware or threats to get into the computer system and exploit it ruthlessly. It slows down the performance of the computer regularly and also hinders Internet accessibility in an improved manner. You will find it hard to use your computer system resources entirely as they were exceedingly confronted by the irritating windows system threats. In fact your important functionalities or other traits related to the system will also be disabled automatically. So, it is recommended to remove static.onlinefastpaydayloan.com popup from computer system as quick it is noticed.
Saturday, April 26, 2014
How to Remove alertfunctions.com Thoroughly: Manual Removal Method
alertfunctions.com a browser hijacker that installs into your computer from unethical way. It is designed to affect almost all browsers including Internet Explorer, Mozilla Firefox and Google Chrome. Once infected, alertfunctions.com is capable of collecting your browsers activity and sends it to remote server promoting related and unwanted ads. Every time you open your browsers, this redirect virus will lead you to the websites associated with this chain. You may not be able to employ any of the computer system tools like Task Manager, Registry Editor or others, as all of them might be deactivated. Moreover, alertfunctions.com also makes path for the other harmful malware or threats to get into the computer system and exploit it ruthlessly. It slows down the performance of the computer regularly and also hinders Internet accessibility in an improved manner. You will find it hard to use your computer system resources entirely as they were exceedingly confronted by the irritating windows system threats. In fact your important functionalities or other traits related to the system will also be disabled automatically. Thus, it is necessary to remove alertfunctions.com and remove its corrupt configurations from your browser.

Friday, April 25, 2014
Is Mostshinstar.com Malware? How to Remove Mostshinstar.com Manually?
 Mostshinstar.com is a nuisance redirect infection that can silently get attached to Firefox, Chrome or Internet explorer, once installed, this virus will hijack your web browser. In this situation, your homepage and search results or clicking on a web link while surfing the web will redirect you to Mostshinstar.com. This redirect virus will disable the genuine antivirus and any security program enters in your computer system or its block your access to any security related websites. Additionally Mostshinstar.com will remove your files on your hard disk and they disturb the innocent user to redirects their personal works through a malicious links. It forces victims to visit some vicious web pages when they visit these fraudulent links and misleading search results. It installs a variety of viruses on the compromised computer. Moreover, the producer of Mostshinstar.com gains money from hacked internet traffic. It is highly recommended that you remove Mostshinstar.com as soon as possible.
Thursday, April 24, 2014
Cannot Uninstall ShopSave.Me - ShopSave.Me Virus Manual Removal
ShopSave.Me has been identified as an adware, which is able to interrupt your browsers when you surf on the Internet. This hazardous adware can infiltrate into its target machines via suspicious websites, spam emails, and other unsafe downloads. It silently gets installed on popular browsers like Chrome, Firefox, IE, etc. Just like other malwares, this one is also used for recommending users discounts. But apart from this, the adware will an extra ordinary infection which keeps record of your browsing habits and collects your personal information which is later on sent to hackers. After ShopSave.Me is installed on your system, something strange will happen frequently. This annoying adware will change the default settings of the registry entries, DNS and the browser. As a result, ShopSave.Me is able to boot up automatically and replace your homepage without approval. Moreover, there will be more and more annoying ads popping up on the screen when you surf the Internet. What really drives you crazy is that this adware will always take up more and more RAM, and then your PC will run slowly as snail. To solve those serious problems, you should remove ShopSave.Me from the system in time.

How to Completely Get Rid of Adware generic_r.KF (Step-by-Step Instructions)
Adware generic_r.KF or Adware generic_r.KG is an adware that hijacks internet browsers and modifies important settings which causes web redirection problems. It displays advertisements within your browser and Flash update boxes with the sole purpose of generating revenue for the cyber criminals. It will disable your browser security and distribute as many threats as possible onto your computer without any permission. Adware generic_r.KF tries tracking your browsing habits and getting some information about what pages you are visiting and what information you are browsing about on the Internet. Such data can be very valuable for marketing companies. Moreover, it may turn out that without your knowledge your computer has become an object of attacks of PC viruses, worms, and malware infections. The aim of hackers is to gain access to your PC and steal your information and money. Hackers will have free access to your log in details, user names, passwords, bank account information and browsing history. Without your knowledge, you will become a victim of credit card and identity theft. Cyber criminals will be able to use all your details for personal purposes. Therefore, it is important not to waste time to remove Adware generic_r.KF from your PC.
Tuesday, April 22, 2014
How to remove Dm.startnow.com from Infected PC? ( Effective Removal Guides)
Dm.startnow.com is a browser hijacker which is designed to promote their search engines and homepage. It hijacks your browser regardless of Internet Explorer, Mozilla Firefox and Google Chrome and exhibits numerous malicious exhibits. It usually gets into your computer when you visit suspicious sites, open junk e-mails, or download free programs from unknown resources. Once Dm.startnow.com intrudes in your operating system successfully, it will add malicious files to the system registry. Then numerous ads would be displayed on the screen during your web browser activities. Some of the ads may induce you to buy some promoted products while some might contain unknown viruses. Dm.startnow.com provides you with irrelevant and useless search results. Besides, your new tabs could be redirected to unneeded websites as well. It may affect your computer’s speed by deleting entries in the registry and other important operating system files. This redirect infection is used for spying targeted computer to record and steal personal user information which can be utilized for marketing or other criminal purposes. Hence, for the safety of your computer, do not hesitate to remove Dm.startnow.com as fast as you can.