Download Popular Antivirus Program

Tuesday, November 5, 2013
Infected With Isearch.omiga-plus.com Virus? Removal Instructions
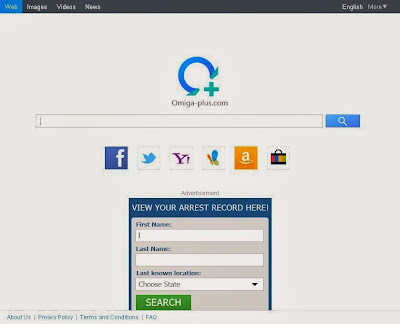
Isearch.omiga-plus.com is a hazardous browser hijacker that invades the target computer with free downloaded from the Internet. It is able to infect the famous browsers including the IE, Chrome and Firefox, etc. it distributes together with many free applications users tend to download online at various resources. If users doesn't pay close attention to the downloading and installation steps of their chosen free software and thus ends up installing various potentially unwanted applications with the Isearch.omiga-plus.com. It uses a deceptive search engine which is crowded with sponsored search results - clicking on such results may lead to malware and virus infections. Once this redirect virus successfully installed on your system, it has ability to change user’s browsers setting such as changing user’s homepage and default search engine. Isearch.omiga-plus.com uses a deceptive search engine which is crowded with sponsored search results - clicking on such results may lead to malware and virus infections. It will automatically load components of malware causing your internet settings to be changed to load Isearch.omiga-plus.com automatically upon opening up a new web browser. Besides, this redirect virus also steals confidential information like passwords, credit card details and etc. for it changes default registry, firewall, DNS and web browser settings without any consent. So it is very important to remove Isearch.omiga-plus.com and all of its components to avoid other damages on your system and protect your precious data.

Sunday, November 3, 2013
The Effective Guide to Remove Rvzr-a.akamaihd.net - Manual Removal Support
Rvzr-a.akamaihd.net is a pop up virus that appears on a computer when its hijacked by a browser infection named http://rvzr-a.akamaihd.net/sd/wrap-0.01.html?u=http%3A%2F%2Frvzr-a.akamaihd.net%2Fsd%2Fapps%2Ffusionx%2F0.0.4.html%3Faff%3D1700-1019. It is a corrupt plugin/extension which can target a Firefox, Chrome or Internet explorer user without his knowledge. Rvzr-a.akamaihd.net may have infected your computer, and then you’ll get to know about this bug when all of sudden you see advertisements by Rvzr-a.akamaihd.net keep popping up on your screen. After getting installed, it has the ability to change the browser settings including default search engine, home page, and privacy settings to take the complete control of your browser. It has the ability to modify the existing registry entries, and create the new corrupt entries so that it can start itself every time you open the windows. It has the ability to change the security settings by disabling the antivirus program installed in your computer due to which the system becomes vulnerable to the other similar threats. It will prompt you to with some fake pop-ups Windows that indicate your system get infect or it needs to software update but it all are scam. Hence, it is very important to remove Rvzr-a.akamaihd.net for your PC safety.
Remove/ Uninstall cdn.optmd.com pop up, Learn How to Delete http://cdn.optmd.com
http://cdn.optmd.com (or cdn.optmd.com pop up virus) is categorized as a very dangerous redirect virus that silently gets infected on popular browsers like IE, Chrome, Firefox and Safari. It is able to redirect your browser to unwanted websites like http://cdn.optmd.com/V2/85105/213900/index.html?g=AQABcfs=&r=www.diynetwork.com/sweat-equity and other same suspicious sites. As a malware sites, http://cdn.optmd.com intrude into your computer without any notice. Once it is installed on your system successfully, this hazardous virus can change the default settings of the browsers. It has ability to alter the default settings of the registry entries, so it is able to boot up automatically and replace your homepage without approval. This redirect virus shows annoying ads popping up on the screen when you surf the Internet. It is quite hard to stop them, for that Http://cdn.optmd.com is still inside your system. Moreover, http://cdn.optmd.com malware will an extra ordinary infection which keeps record of your browsing habits and collects your personal information which is later on sent to hackers. So, http://cdn.optmd.com virus is extremely harmful infection which must be removed to keep your systems safe.
Saturday, November 2, 2013
Remove DriverUpdates.net - Completely Delete and Get Rid of DriverUpdates.net
DriverUpdates.net is a tricky and harmful browser hijacker which pretends to be a legit and helpful search provider. It is able to collect non-personal information that is provided by browsers, including Internet Explorer, Google Chrome, and Mozilla Firefox. it can collect information about the website you visit, what items you click on, and what advertisements you find on particular websites. Once infected, DriverUpdates.net redirect virus will then make modifications to the original browser settings furtively. It takes the control of your Google Chrome, Internet Explorer, and Mozilla Firefox. Your default home page and search provider will become DriverUpdates.net. Moreover, DriverUpdates.net hijacker changes the Windows registry keys. It will be able to run in the background every time the machine is launched. This redirect virus can take up a lot of system resources when running at the back. That will lead to the slow performance of the whole Operating System. The Internet connection shuts down sometimes. What’s worse, DriverUpdates.net browser malware has the ability to trace your online actions to gather your important information. Therefore, it is recommended to remove DriverUpdates.net virus as soon as you notice its first ads on your computer.
Guide to Remove www.Nv83.info Manually and Effectively--- How to delete http://nv83.info/adw234028/lp9a6/out.php?ubn=iewin764&keyword=adw_testa5_lp9a6_linkedin.com
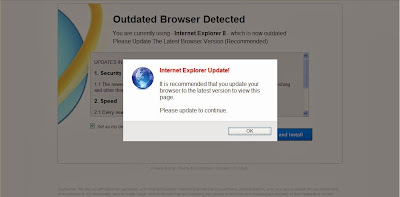
www.Nv83.info is an infamous browser hijacker that changes your homepage and default search provider without your knowledge. It displays numerous advertisements on Internet Explorer, Mozilla Firefox and Google Chrome browsers. www.Nv83.info mainly interrupts when you are making some search on your browser. It adds various sponsored websites such as http://nv83.info/adw234028/lp9a6/out.php?ubn=iewin764&keyword=adw_testa5_lp9a6_linkedin.com to your search results and displays ads about computer protection. As it consumes lots of your system resources, your system becomes considerably slower. Once infected, www.Nv83.info will inform that you should update your browsers because your browser is Outdated. The warning said Outdated Browser Detected. However, when you follow the steps to update your browser, you will be found that www.Nv83.info redirects you to its own sites and also redirect the searches to irrelevant address. Default settings will be totally changed and all the time you will be redirect to infective location. Moreover, it is able to collect the terms of search queries, recording browsing history and gather personal data such as IP address, name, email address, telephone number, etc. it also opens the door for other malware infections to affect your PC performance further. This redirect virus occupies lot of your system resources result in dragging your computer and crashing your browser. Thus, in order to protect your computer from the deep damage, it needs to remove www.Nv83.info without any delay.
Friday, November 1, 2013
Need Help to Remove Intext.nav-links.com Completely: Manual Removal
Intext.nav-links.com is classified as a harmful browser hijacker that changes default settings without permission. It invades into your system when you visit suspicious websites, click malicious links, or download unverified free programs, etc. once executed, it has ability to change the default home page or web browser search engine automatically. It redirects web search queries to unwanted sites or manipulated results. It also it has the ability to escape from the detection and deletion of your antivirus tools. This redirect virus always changes its files to ensure its malicious registry disturb the whole system. As an annoying redirect virus, Intext.nav-links.com will hijack your web browsers such as Google Chrome, Internet Explorer and Mozilla Firefox to set itself as your default homepage and search engine. Once it starts, there will be with lots of irrelevant and sponsored links instead of useful and informative search results. Moreover, Intext.nav-links.com causes a lot of web redirects to promoted web pages with lots of floating ads and commercial products. If you accidentally click any of the offered links, you would be led to the installation of additional risky viruses like Trojans. What’s more, Intext.nav-links.com virus monitors your keystrokes and gathers your important information. Then the collected data will be sold to some web criminals for illegal purposes like carrying out commercial activities or delivering spam emails. Therefore, it is necessary to remove Intext.nav-links.com immediately to keep a safety network on your computer.
Easily Remove PUP.Optional.CouponScout.A From Your Computer, Virus Removal
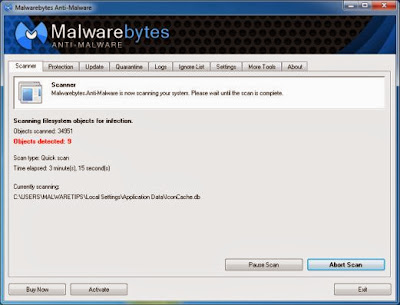
PUP.Optional.CouponScout.A is identified as a dangerous adware that sneaks into your system without your knowledge or permission. It is a Potentially Unwanted Program by MalwareBytes Anti-Malware because it inflicts and acts as a malicious threat into your computer system. Once infected, PUP.Optional.CouponScout.A will be appended to your browser as a plugin. When you start your system, you homepage will be changed into other unknown websites with numeral pop up ads. Most of this suspicious websites connect to unreliable websites which contain potential threats. It is not easy to uninstall this malware because this type adware is able to avoid the deletion via modifying system settings. As a tricky adware, it injects its codes to the registry, and it is able to drop other malware onto your computer. It slows down your system performance to make your computer freezing easily during web browsing tasks. Since your security applications are affected by the adware, they just perform badly and fail to catch any type of computer threats entirely. In addition, the infected computer will be at risk because the adware creator has ability to collect user’s confidential information and records. Therefore, it is important to remove PUP.Optional.CouponScout.A as soon as possible to make sure your machine is running in safe network environment.
How to Remove CampusLeader.com Hijacker? Manual Removal
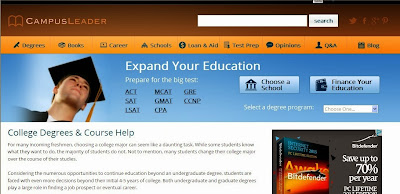
CampusLeader.com is a browser hijacker redirect virus which disguises itself as a useful search website such as Google, Yahoo and Bing. In reality it is a malicious links that can change your internet settings without the user content. It gets into the famous browsers including the IE, Firefox and Chrome to replace current homepage link and search provider. Once your browsers get infected by CampusLeader.com, the browser is taken by this redirect virus. When you open a new tap or visit the desired websites, you will be redirected to CampusLeader.com or other related website. And then there will be lots of annoying ads displaying on your screen to disturb your regular activities on the Internet. At the same time, the default search engine will be replaced. Whenever you type in a search, all the links shown on your search results will be redirected to CampusLeader.com and many other advertising sites. Besides, this redirect virus may introduce many other risky viruses on the other hand. You should know that the longer you keep this dangerous virus inside the system, the worse it will be. This nasty virus can even trace your online activities and gather your private data for its designers. Thus, it is highly advised to clean up CampusLeader.com to protect the PC from damage.