Download Popular Antivirus Program

Showing posts with label ransomware. Show all posts
Showing posts with label ransomware. Show all posts
Friday, January 10, 2014
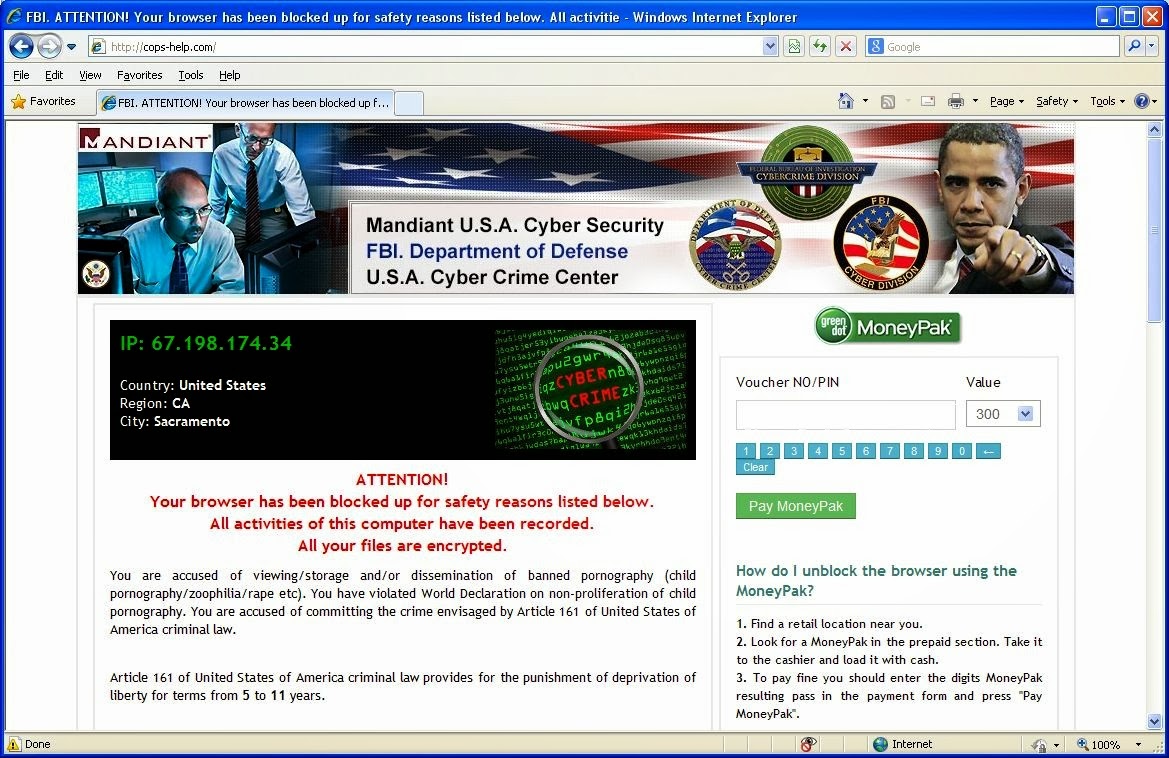
Learn to Remove Cops-help.com Step by Step (Virus Removal)
Cops-help.com is a malicious threat that is found as ransomware. It is made by cybercriminals with the only purpose to pilfer money from unwary computer users. Once infected, your currency browser will be blocked by showing a bogus pop-up image to scare computer users into believing they have performed numerous illegal online cybercrime actions. This fake webpage intimidates target computer users into thinking it is an official warning message. The false alert of Cops-help.com Ransomware accuses PC users of committing cybercrime activities and states that they have breached certain laws. The fake warning message of Cops-help.com Ransomware declares that the PC user has been downloading and spreading copyrighted material to other computer users, watching and dispersing child pornography, sending spam emails or visiting malicious websites connected with terrorist organizations. The misleading notification of Cops-help.com Ransomware lists instructions on how to pay a so-called ransom of 300$ via Ukash or Paysafecard to unlock the computer and evade arrest. Computer users should not pay the so-called ransom for supposed cybercrime activities because this won’t help them to regain access to their computers. Victims should remove Cops-help.com Ransomware instead of paying it.

Monday, December 23, 2013
How to Remove Policesavealert-secure.com Ransomware? Policesavealert-secure.com Manual Removal
Policesavealert-secure.com is one of deceptive ransomware that displays a lock screen on your browsers that requires you to pay a ransom. This new variant from the MoneyPak virus family is another long-lasting scam virus released recently to help computer hackers collect fines from innocent PC users. Policesavealert-secure.com totally locks down the infected computer and displays a scary warning message in the middle of the screen claiming that the work on your computer has been suspended on the grounds of unauthorized cyber activity. Because violations of the law such as distribution of pornographic files, visit the websites of terrorist groups, distribution of virus programs, etc. Policesavealert-secure.com can be noticed that to unlock your browses and to avoid other legal consequences, you are obligated to pay a release fee of $300. Once this virus is installed in your system it will completely lock you out of your browsers and states that All your files are encrypted, however, it is a fake message. It also has detected that your computer has been involved in illegal cyber activity. Usually, this ransomware can spreads through the file sharing, freeware downloading, visiting unknown sites, playing online games and others. Furthermore, to make this alert seem more authentic, this virus also has the ability to access your installed webcam, so that the bogus notification shows what is happening in the room. Remove Policesavealert-secure.com as soon as possible once detected to ensure the safety of your system.
Wednesday, August 21, 2013
Remove/ Uninstall West Mercia Police Ukash Virus, Learn How to Delete West Mercia Police Ukash Virus
West Mercia Police Ukash Virus is one new version of famous ransomware that targets computers in the United Kingdom and locks you out of your Windows desktop. As a fraud program, it was created for the purpose of deceiving computer users to purchase licensed version of software. West Mercia Police Virus is fake antivirus software. It mainly attacks the computer users in UK and pretends to be from UK police. It locks your windows desktop and demands to pay a fine of 100 pounds via Ukash/ Paysafecard stated as prepaid payment systems to unlock your computer. Once it gets installed it will automatically start the computer and found many malwares that it does not remove until you purchase the licensed software. This virus shows false scan results and fake security warnings to persuade users to think that the computer is infected with virus. This virus also blocks access to any security-related Web sites and slowing down the computer as soon as it infects the computer. To be worse, West Mercia Police Virusis designed by the cyber criminal to steal your confidential like bank details, credit card no. etc. which is later used for various illegal activities. So it is strongly recommended to remove West Mercia Police Ukash Virus as soon as possible.
Tuesday, August 13, 2013
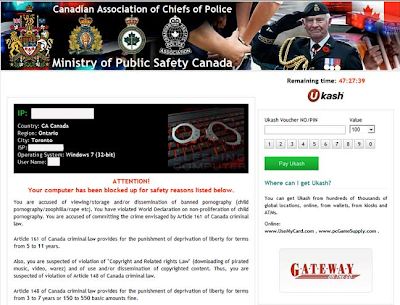
The Effective Guide to Remove Canadian Association of Chiefs of Police virus - Manual Removal Support
Canadian Association of Chiefs of Police Virus, (also known as Ministry of Public Safety Canada virus or CACP Virus) is classified as ransomware that scares computer users into paying a non-existing fine of $100 CAD within 48 hours through Ukash or Paysafecard voucher. The Canadian Association of Chiefs of Police ransomware pretends to be a lock screen placed on your computer by the Ministry of Public Safety Canada, and Interpol that states that it has detected that your computer has been involved in illegal cyber activity. Once infected, the Canadian Association of Chiefs of Police virus firstly locks your computer screen. A webpage which requires you to pay a fine covers the whole desktop of the compromised computer. It seems that the computer is really locked and it is useless to press any key. Actually, the Canadian Association of Chiefs of Police virus sneaks into the computer to encrypt the system files of the compromised computer. As long as this virus stays in your computer, No matter how many times or when you boot your computer, you still can’t access to the desktop, application and files. However, you should realize that the Canadian Association of Chiefs of Police lock screen is a scam, and you should ignore the alert from it. There is no need to pay cyber criminals a ransom of $100 CAD since it wouldn't help to unlock your computer. The only way to get around is starting your computer for a different user with administrative privileges if you have created one before. Otherwise, you need to reboot your system from external uninfected source and then remove Canadian Association of Chiefs of Police virus manually.
Friday, July 19, 2013
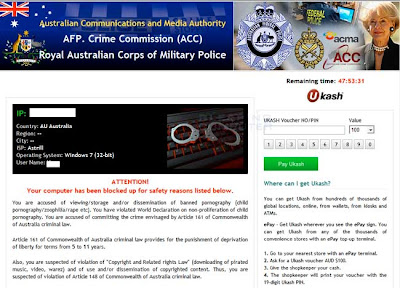
Learn to Remove Australian Communications and Media Authority (ACMA) virus Step by Step (Virus Removal)
Australian Communications and Media Authority (ACMA) virus is a group of ransomware that uses the name of the government department to get users money in Australia. This virus locks victims computer and show a lock screen that requests a ransom of AUD $100 by Ukash before you can access your Window desktop. The ransomware program targets the Australian computer users in the names of the Australian Communications and Media Authority (ACMA), AFP Crime Commission (ACC), Royal Australian Corps of Military Police, and Interpol to scare its victims that your computer has been involved in illegal cyber activity. It is important to realize that this computer virus is only scam which can be ignored because the real government will not use this way to notice the people who have broken the laws. Let alone lock the users’ computer. The virus maker will plant this ransomware into the free program so that the victims’ computers are easily infected. When this type malware installed on the computer, you can’t do anything except on the screen is a fake warning that says you have violated laws and thus computer is locked up as a punishment. Moreover, this virus can slow your computer performance, and it can cause many serious computer problems. So when you suffer this situation about lock screen, you should not pay a fine to this virus. To get your computer in normal function, the effective way is manual removal this virus.
Sunday, July 14, 2013
Need Help to Remove Mandiant U.S.A Cyber Security Completely: Manual Removal
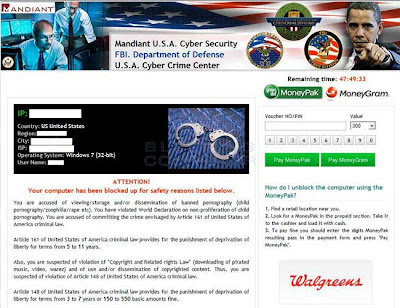
Mandiant U.S.A. Cyber Security is one type of Ransomware which displays a lock screen when you start Windows. It requires computer users among the United States areas to pay a ransom before you will be allowed to access your Windows desktop, applications, or files. It pretends to be Mandiant, the FBI, USA Cyber Crime Center, Department of Justice, and Interpol to block computers to get the victims to pay a fine in the amount of $300 within 48 hours. To make the victims firmly believe, this Mandiant U.S.A Cyber Security ransomware can state the reasons why your computer was blocked, such as the distribution of pornography, copyrighted files, or computer viruses, and it can list personal information like IP, Country, Region, City, Operating System and User Name etc on top left corner of the screen. The malware creators claim that you can access your Window desktop again when they receive the money through MoneyPak or MoneyGram voucher. Computer users log on to hacked or malicious sites online, download unknown spam attachments or install unfamiliar programs, they could get the chances to be infected by this tricky Ransomware. It is important to ignore this because Mandiant U.S.A Cyber Security is a computer inflection. It does not let your computer get right even if you pay for the fine. So when you suffer this problem, you should remove this Mandiant U.S.A Cyber Security ransomware quickly.
Tuesday, April 30, 2013
How to Remove Joint Chiefs of Staff Virus Significantly - Joint Chiefs of Staff virus Removal Help
Joint Chiefs of Staff virus is a highly loathsome ransomware that right now is doing evil things on users' computers. Typically with other scam programs like FBI moneypak, Department of Justice and Metropolitan Police, Joint Chiefs of Staff is to block users out of system with the full screen of warning message that misleadingly in the name of legitimate institution. Usually, the imaginary message will indicate that the activities users used to take have been classified to associate with child pornography, copyrighted music, video and illegal programs. Judging from the laws, you will be required for a penalty of 400 USD in 48 hours to get the computer unlocked. Otherwise, you will be prosecuted and put into jail. Be aware that this can definitely not to be trusted though it looks seriously as real. The only goal for this dangerous virus is to trick money from your account. It is meaningless for users to do that. To get back your clean PC, Joint Chiefs of Staff virus must be removed immediately from the moment it has been detected. Only in this way can your computer release from severe troubles. Here comes the original quotation of the warning message:
